
 ">WeChat
A brief recent review of Volatility, an open-source forensic framework that allows for the analysis of exported memory mirrors, access to memory details and operational status by accessing core data structures, using plugins, direct dump system files, screenshots, viewing processes etc. ~ data examples
Cridexemdump.zip gets cirdex.vmem with a command to view mirror information, volatility-fcridex.vmem imageinfo=WinXPSP2xpslidex.vm_profile=WinXPS2x86pslistSee ProcessVolatility -fridex.vm-product=WinXPPSP2x86 netscan access the network volatility -fcridex.vmem-profile=WinXPSP2x86 psxxxpxxpxxpxxxpxxpxpxpxxpxpxpxpxxpxpxxpxpxptxpxpxpx.vm-product=WinXPSP2xppxgrxpxpxphxpxpxxpxpxpxpxpxpxpxpxpxpxpxxpxxxxxxpxxxspxxxxxxxxxxxxpxxxxxxxxxxxxxtxxxxxtextxx Volatility -f cridex. vmem -profile=WinXPS2x86-pid=584 dlldump -D/tmp and then cd/tmp uses ls and then md5sum mobile 584.24a054840a68000.dll obtain 335c6fbf298b5b4c188bc9cb26ece authentication of hash tohttps://www.virustotal.com/gui/home/upload orhttps://www.hybrid-analysis.com/ Analysis of malwarecidex infection.
0x01 Installation
Installation divided into three steps:
- Download
- Install necessary python dependent files
- Install Body
Download
You can be there.Release中找到对应你系统(Mac,Win,Linux)的源代码,当然也可以通过github去获取源码:
git clone https://github.com/volatilityfoundation/volatility.git
Dependency
Do not install these dependencies if only using Volatility, but if you want to use some plug-ins, you need to install them.
Distorm3:A great inverted repository.
pip install distorm3
Yara:Malicious software classification tool
pip install yara
PyCrypto:Encryption Toolset
pip install pycrypto
PIL:Photo Processing Library
pip install pil
OpenPyxl:Read and write excel files
pip install openpyxl
ujson:JSON DRIVING
pip install ujson
Install
If you use a stand-alone win, linux, mac execution file, you don’t have to install it. Just do it with python. If you download the compression file, you can either run the python master or install Volatility in the specific location of the system in one library using python setup.py install, so we can then use Volatility as a repository to quote namespace from other scripts.
0x02 Usage
Kali had a volatility, so I ran it directly at Kali Hill and here I’m using an example of the CTF that I’ve been reading for two days.
Imageinfo
This command can be used to extract summary information from memory mirrors, such as system versions, hardware architecture, etc.
volatility -f wuliao.data imageinfo
By Suggested Profile(s), we know that the version of this mirror file is most likely to be Win 7SP1x64.

Use –info parameters to view the information of Volatility added program and plugins
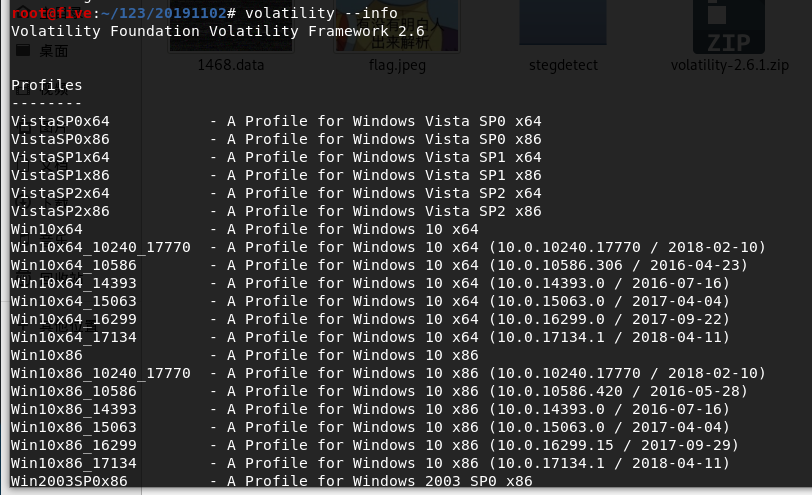
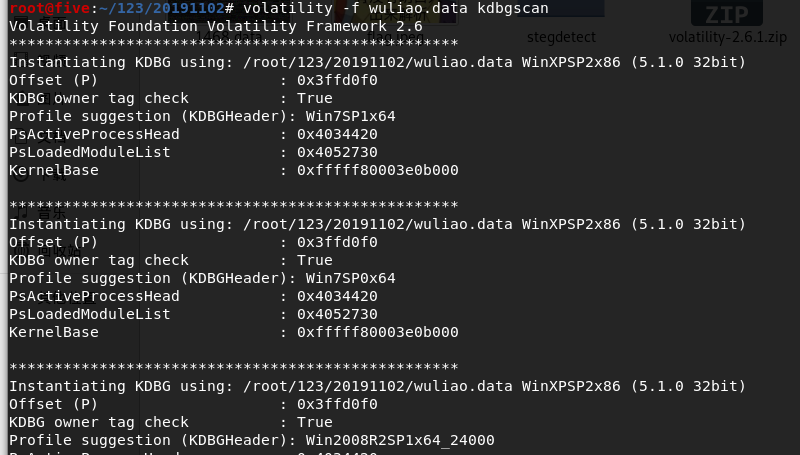
Kdbgscan
The value of this plugin to scan files is usually multiple, with only one result being perfectly correct.
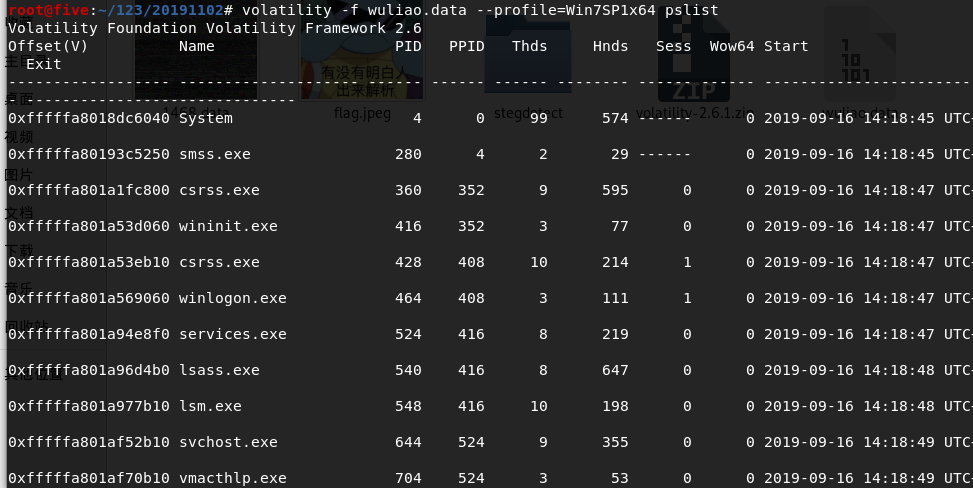
Pslist
volatility -f wuliao.data --profile=Win7SPx64 pslist
pslist can directly list the running process and if it is finished, the date and time will be shown in Exit column indicating that the process has been completed
Hivelist
Lists the register in the slow memory
volatility -f wuliao.data --profile=Win7SP1x64 hivelist

filescan
Scan Files in Memory
volatility -f wuliao.data --profile=Win7SP1x64 filescan
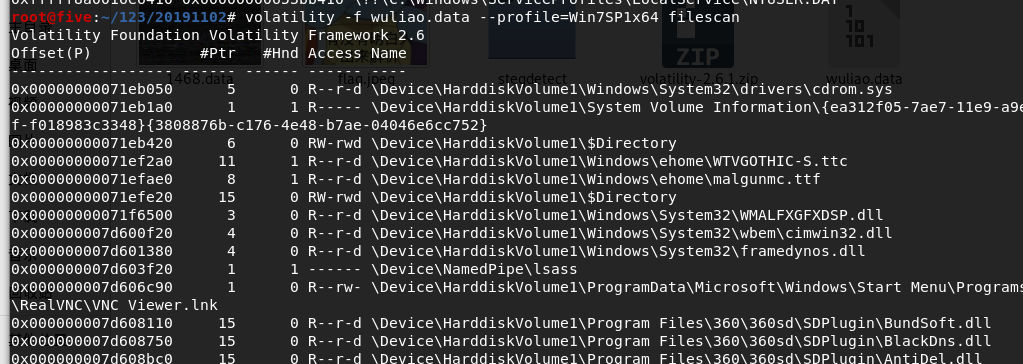
Filecan can also screen with grep commands, for example.
volatility -f wuliao.data --profile=Win7SP1x64 filescan |grep "doc\|docx\|rtf"

Yeah.
volatility -f wuliao.data --profile=Win7SP1x64 filescan |grep "flag"

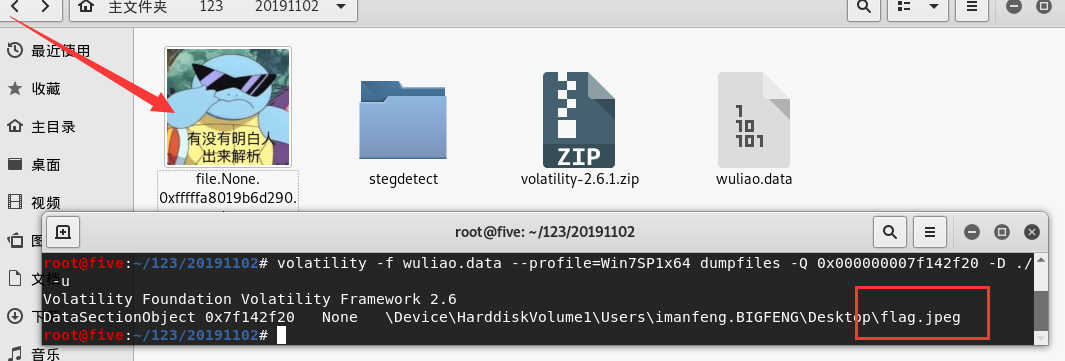
Dumpfiles
Exporting cache files in memory I directly export the flag.jpeg file from search above
volatility -f wuliao.data --profile=Win7SP1x64 dumpfiles -Q 0x000000007f142f20 -D ./ -u
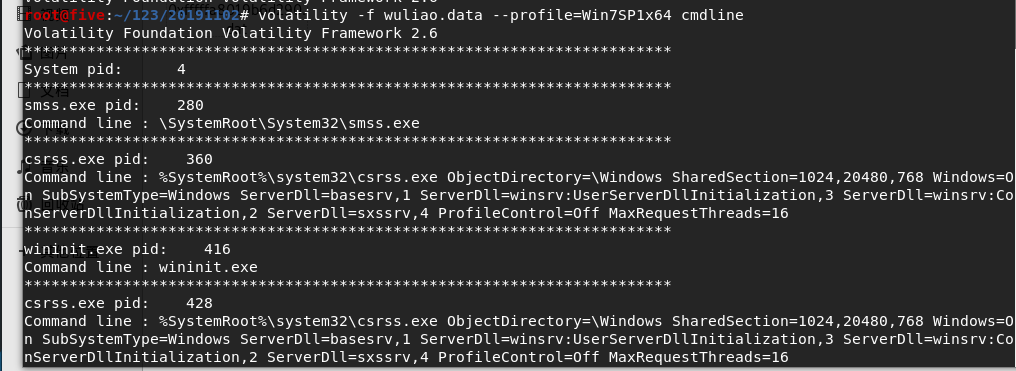
Cmdscan/cmdline
Extracting cmd commands from memory
volatility -f wuliao.data --profile=Win7SP1x64 cmdline
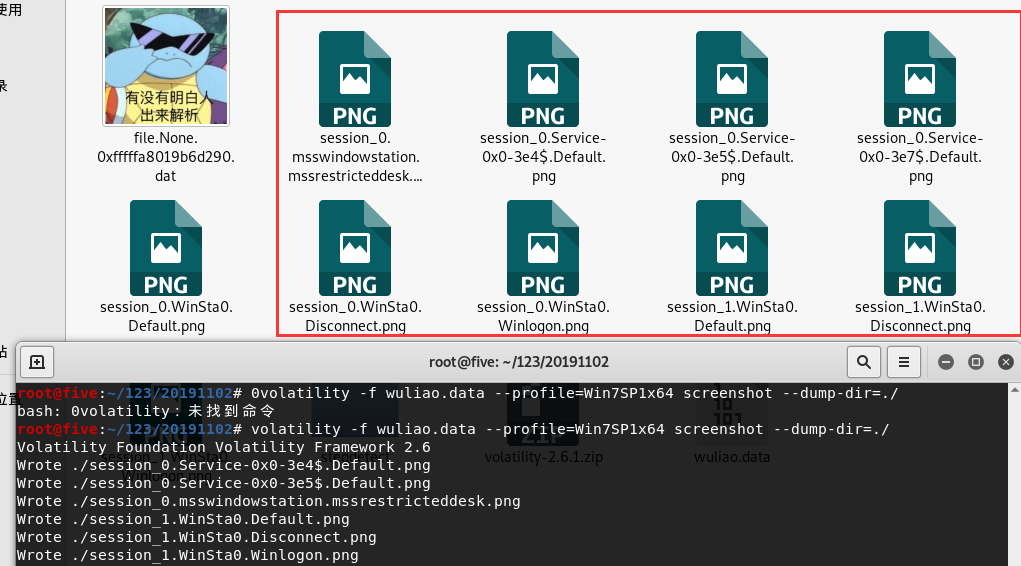
View screenshot
volatility -f wuliao.data --profile=Win7SP1x64 screenshot --dump-dir=./
View system usernames
volatility -f wuliao.data --profile=Win7SP1x64 printkey -K "SAM\Domains\Account\Users\Names"
View Network Connections
volatility -f wuliao.data --profile=Win7SP1x64 netscan

未经允许不得转载:萌萌Apprentissage » Volatility, an open source forensic framework -- export memory mirrors -- analyze the virus process


 linux One Chinese script
 Google shell enable enhanced mode 4 nuclear 16G RAM
 Tmux use tutorial
 Screen's summary
 I'm gonna get you a new one, shell.cloud.google on the line.
 Linux Memory Clearing

