
 ">WeChat
Infiltration tests are simulations of a cyber attack, where hacker hacking networks detect weaknesses before the real hacker invades. Like the film Sneakers, hacker consultants break into companies to discover network vulnerabilities.
Back in the old days, hacking was a very difficult thing to do, and required a lot of manual work. Today, however, an entire set of automated testing tools seems to have transformed hackers, who can even enhance computers’ performance and perform more tests than they used before.
I. Kali Linux
Kali is a basic infiltration test operating system that most people use, unless they have sophisticated knowledge or special circumstances. Kali, formerly known as BackTrack Linux, maintained by excellent personnel of the Office Security (OffSec, OSCP certification), has now been optimized in various ways to be used as an attack tool for permeating testers.

II. Nmap
Nmap is an abbreviation for the web scanner, which is extended to end-of-port scanners. As a proven penetration test tool, almost everyone can use it. Which ports are open? What are operating on these ports?
III. MEtASPLOIT
When you can use Metasploit, why is there a loophole? The software is like a bow and arrow: aim at the target, select a hole, choose a payload, and then launch. For most permeability testers it is essential that metaploit automatically do much of its former cumbersome work, which is “the world’s most widely used penetration testing framework.” An open source project supported commercially by Rapid 7, Metasploit, is an essential tool for defenders to ensure their systems are protected from attack.
IV. Wireshawk
Wireshark is an all-encompassing tool for understanding the flow of traffic across networks. Although it is usually used to study daily TCP/IP connections, Wireshark supports analysis of hundreds of protocols, including real time analyses and declassification support for many of them. If you are new to penetration testing, Wireshark is a tool that must be learned.
五、John the Ripper
John here is not a Victorian London serial killer, but will crack the password at your GPU operation speed. The password breaker is open-source and used to decipher it. John uses a list of possible code words, and then “@” replaces “a” with “5”, or it can be converted in such a way that powerful hardware runs indefinitely until the password is found.

VI. Hashcat
“The world’s fastest and most advanced password restoration practical program” may not be enough to describe Hashcat, whose value is naturally well known by the users. Hashcat can go up against John the Ripper. It is a first-choice penetration test tool for breaking al-Hashi’s code, and hashcat supports multiple surmise attacks, including dictionaries and mask attacks.
VII. Hydra
Hydra is a similar tool for John the Ripper, which can be used to break passwords online (e.g. SSH or FTP login, IMAP, IRC, RDP etc.). HYDRA is used in specified cracking services, and if necessary you can enter word lists and then start breaking them. Tools such as Hydra remind people that limiting passwords and disconnecting user connections can successfully resist an attack after a series of logging attempts.

VIII. Burp Suite
If you do not mention the Web Gap Scanning Program Burp Suite, discussion of penetration testing tools is incomplete, and Burp Suite, unlike other instruments mentioned so far, is a paid, expensive tool that professionals have used to use. Although there is a Burp Suite community version, it lacks many functions, and Burp Suite’s business version costs $3999 per year.
九、Zed Attack Proxy
Those who do not buy Burp Suite will find Zed Attack Proxy (ZAP) of the OWASP almost as effective as it is, a tool that is completely free. By definition, ZAP places itself between browsers and testing sites (also known as intermediaries), allowing for interception traffic to be checked and modified. It lacks many details about Burp, but its open source licences are easier to deploy on a large scale and cheaper. For starters, it is a very good tool for understanding the vulnerability of network flows.
X. Sqlmap
This very effective SQL injection is an open source that “automated the process of detecting, using SQL to plug holes and take over a database server.” The targets for Sqmap include MySQL, Oracle, PostgreSQL, Microsoft SQL Server, Microsoft Access, IBM DB2, SQLite, Firebird, Sybase, SAP MaxDB, Informix, HSQLDB, and H2. People in the past had to use Hot Needle to inject SQL into hard disks. Now, sqlmap needs no such degree of success in your daily work.
XI. Aircrack-ng
If you want to test the safety of your client’s wifi or family wifi, it is fine with aaircrack-ng. This wifi security clearance tool is free, but users can buy their own Pringles antennas. Today, wifi may be destroyed by poor configuration, wrong passwords, or outdated encryption protocols. With or without pringles’ “antray,” Aircrack-ng remains the preferred option for many people.
未经允许不得转载:萌萌Apprentissage » Eleven tools for penetration testing professionals

 learn NMAP
 View all Linux command execution orders and numbers
 The linux restart could not start the linux software to remove reload xrdp reload

 Linux takes a summary of the positions in power.
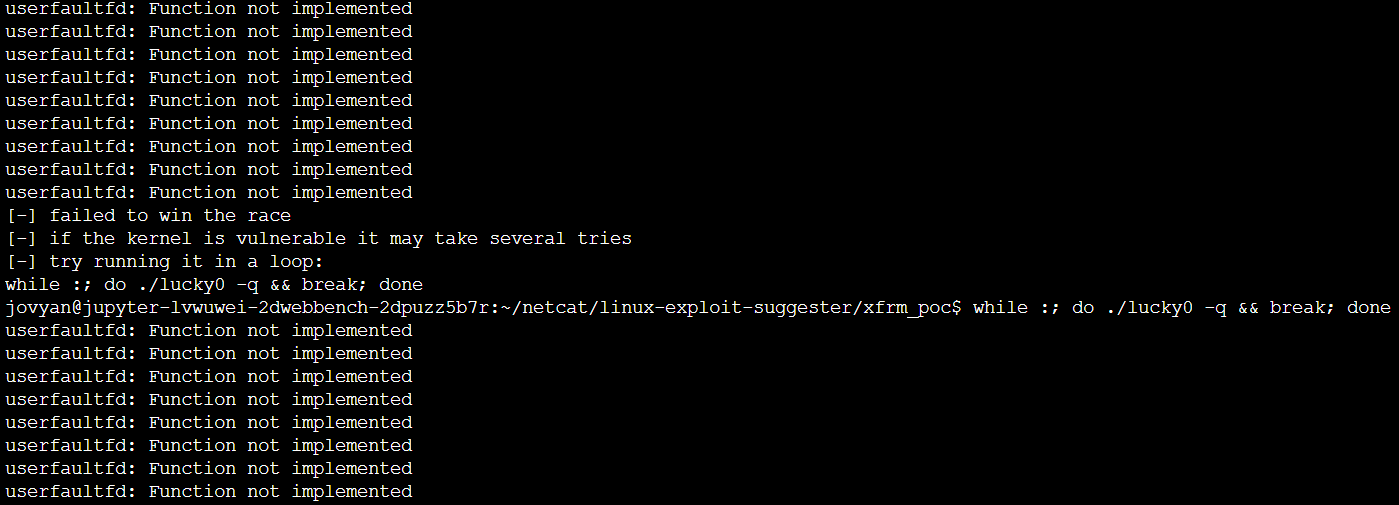 Post-infiltration of the latest Linux power root, [CVE-2019-15666] XFR_UAF affects most versions of the linux core
 The 100-degree cloud disk is downloaded using the linux server proxy

